المعذره فلا أجيد ترجمة المقالات العلميه التي أكتبها للعربيه.
هذه مقالة قمت بكتابتها عن قضية تتبع سرقة البيانات من الشرائح الالكترونية لخدمات الجوال.
SIMbrush is a Digital Forensics tool used to investigate SIM cards in GSM Systems only. The digital forensics will follow preservation, collection, validation, identification, analysis, interpretation, documentation and presentation of digital evidence derived from digital sources.
According to this process, the SIMbrush tool can be placed in the imaging technologies group of techniques in relation to the preservation phase
The idea of this tool it is placed as Interface between Mobile Equipment (ME) and Subscriber Identity Module (SIM) to collect the data from the SIM card.
SIM Cards has an alarm system against any intrusion attempt of the encrypted data, SIMbrush will not use any black hat techniques, as the only information that a smart card offers to the outside world is the data inside its filesystem, SIMbrush tries to extract it.
The file system in SIM Card has a root called Master File (MF). DF and EF are also other forms of file system which can be accessed using SIMbrush.
The algorithm SIMbrush use set of commands to interact with the filesystem: SELECT, STATUS, READ BINARY, UPDATE BINARY, READ RECORD, UPDATE RECORD, SEEK, INCREASE, GET RESPONSE
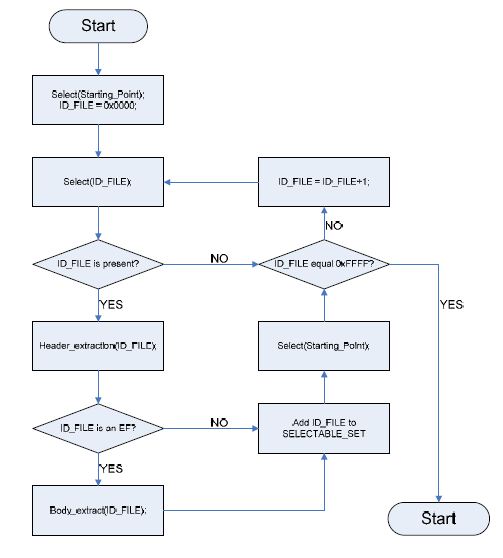
The above commands will be used to access to obtain the header of every file present in the filesystem of the SIM with a single scan of the ID space. the standards define the concepts of current file and current directory. The current file is simply the last successfully selected file. The current directory is the last successfully selected DF, or the parent DF of the current file, if the current file is an EF: it defaults to MF and may coincide with the current file.
The below flow chart simply show the process of how SIMbrush algorithm works: